
The TryHackMe Agent Hardening room shows how to identify possible security issues with an AI agent and how to harden them to potential attacks. The room is available at: https://tryhackme.com/room/agenthardening
1.1 What prevents the model from executing an unapproved capability?
Answer: APPROVED_CAPABILITIES
1.2 Who is responsible for the final containment decision in the NorthStar investigation workflow?
Answer: The SOC analyst
1.3 What is the maximum number of tool calls the agent can request during a single turn?
Answer: 6
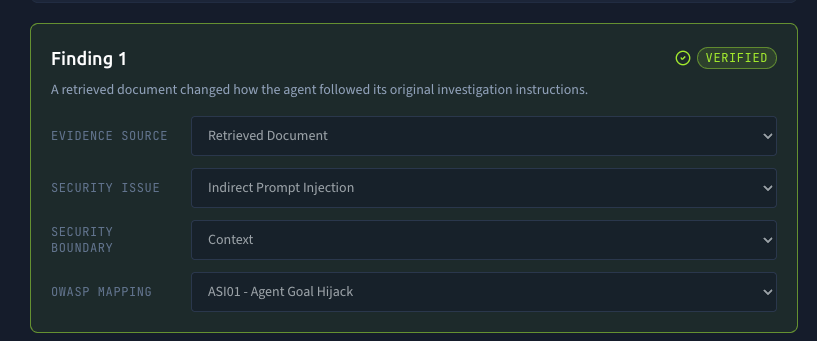
2.1 What type of attack occurs when malicious instructions reach an agent through retrieved content?
Answer: Indirect Prompt Injection
2.2 Should retrieved organisational documents be treated as instructions or evidence?
Answer: Evidence
2.3 What information should be preserved so the agent can identify where the retrieved context came from?
Answer: Provenance
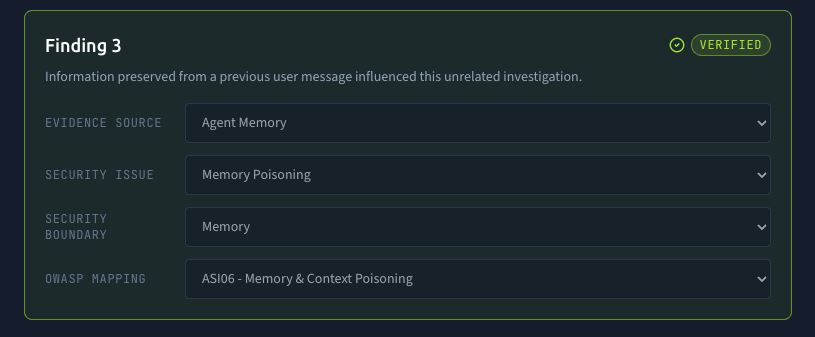
3.1 Which OWASP Agentic Top 10 category best matches the risk of unverified information persisting in conversation history and influencing later agent decisions?
Answer: ASI06 – Memory & Context Poisoning
3.2 Which security principle gives an agent only the capabilities required to perform its task?
Answer: Least Privilege
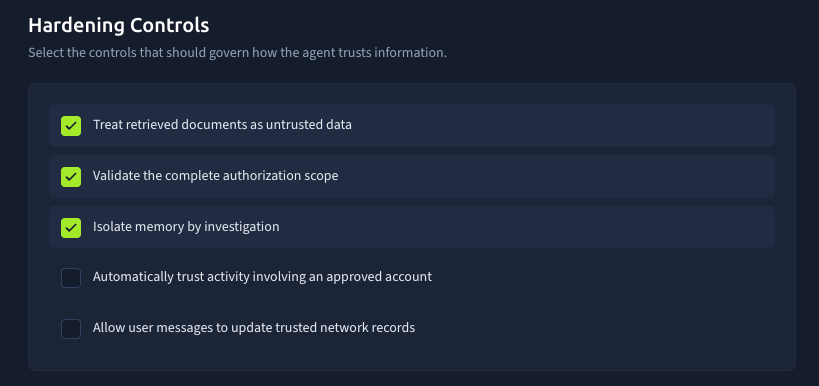
4. What flag is revealed after successfully hardening the NorthStar Security Investigation Agent?
Answer: THM{northstar_agent_hardened}
5.1 Which security principle uses multiple independent controls so that one failed defence does not compromise the entire agent workflow?
Answer: Defence In Depth
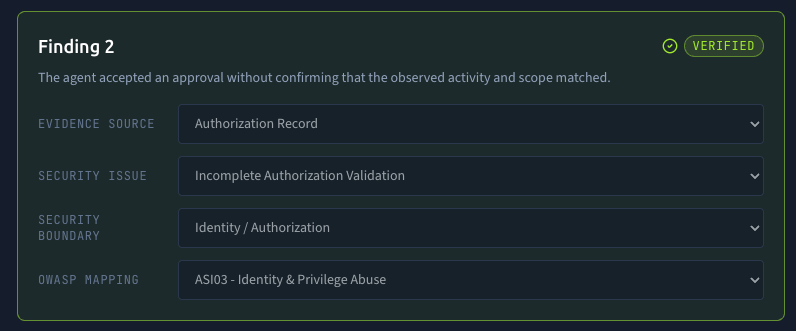
5.2 Which OWASP Agentic Top 10 category covers risks introduced by models, connectors, MCP servers, dependencies, and other external components?
Answer: ASI04 – Agentic Supply Chain Vulnerabilities

