The TryHackMe Understanding Vulnerability Databases Room is a free room from TryHackMe that explains what Vulnerability Databases and how they are useful. The room is available at: https://tryhackme.com/room/understandingvulnerabilitydatabases
- Do vulnerability databases connect vulnerabilities, their associated exploits, and available patches? (yea/nay)?
Answer: Yea
2.1 What classification system groups vulnerabilities based on their root cause?
Answer: CWE
2.2 Which standardised naming scheme is used to identify affected vendors, products, and versions precisely?
Answer: CPE
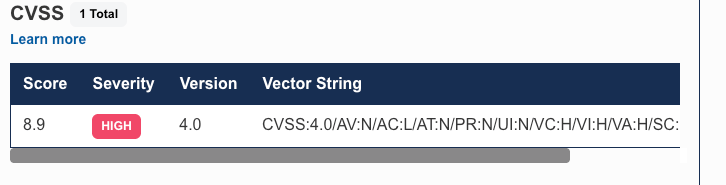
3.1 What is the CVSS score for the vulnerability?
Answer: 8.9
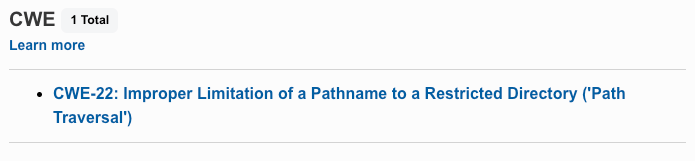
3.2 What is the CWE number for the CVE-2026-22871?
Answer: 22
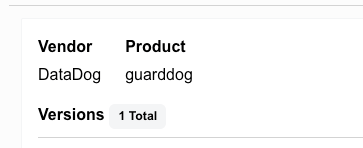
3.3 What is the vendor name for the CVE-2026-22871?
Answer: DataDog
4.1 Which vulnerability database enriches CVE entries with structured CPE mappings and tagged exploit references?
Answer: NVD
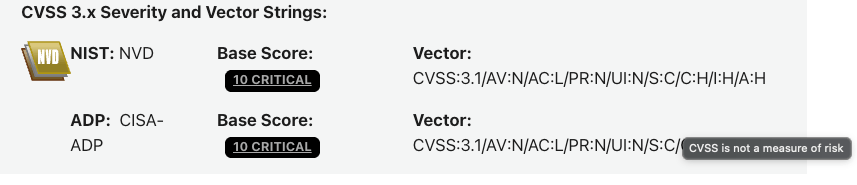
4.2 Using the NVD, what is the CVSS v3.1 base score assigned to CVE-2021-44228?
Answer: 10.0
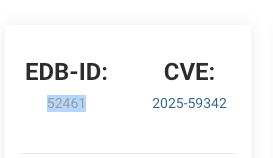
5.1 What is the EDB-ID associated with CVE-2025-59342?
Answer: 52461
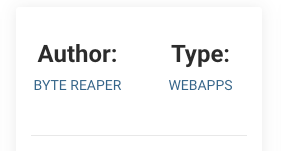
5.2 What is the author’s name for the exploit with CVE-2025-59342?
Answer: Byte Reaper