
The TryHackMe MS Sentinel: Ingest Data is MAX only subscriber room from TryHackMe and is part of their Defending Azure Training Path. The room is available at: https://tryhackme.com/room/sentinelingestdata
- What is used to ingest log data into Microsoft Sentinel?
Answer: Data Connectors
2.1 Are data connectors specific to each data source? (Yea/Nay)
Answer: Yea
2.2 Data connectors are available in how many ways?
Answer: 2
3.1 What are bundles of data connectors, workbooks, analytic rules, and playbooks called in Microsoft Sentinel?
Answer: Solutions
3.2 Content source can either be a Solution or?
Answer: Standalone
4.1 What Content source type is Microsoft Entra ID?
Answer: Solution
4.2 What category is the Microsoft Entra ID?
Answer: Identity, Security – Automation (SOAR)
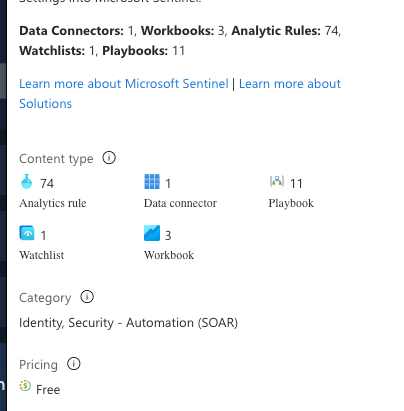
5.1 Where can you find all the details about a connector?
Answer: Connector Page
5.2 In order to configure the Microsoft Entra ID data connector, what permissions are required on the Log Analytics workspace?
Answer: Read And Write
6.1 What does the Microsoft Defender Threat Intelligence (MDTI) connector import?
Answer: Indicators of Compromise
6.2 Can threat indicators include IP addresses and domains? (Yea/Nay)
Answer: Yea

