
The TryHackMe Building Wazuh Rules Room is a subscriber only room from TryHackMe that focuses on how to create detection rules for Wazuh. The room is available at: https://tryhackme.com/room/buildingwazuhrules
1.1 What decoded (parsed) field contains the value tryhackme.com?
Answer: website
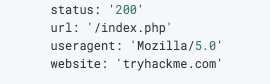
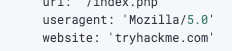
1.2 What is the last field extracted by the thm-web decoder?
Answer: useragent
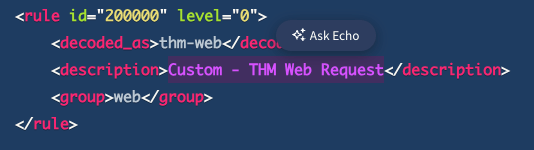
2.1 Which rule description was applied to the third tested web event?
Answer: Custom – THM Web Request
2.2 Review the prebuilt Wazuh rules in the Rules panel.What is the regex query for the rule that detects PSEXEC?
Answer: (?i)PSEXESVC.exe
3.1 What MITRE tactic do you see in the Ruleset Test output for the brute-force alert?
Answer: Credential Access
3.2 Which IP address matched the CDB list and generated a “Bad IP” alert?
Answer: 158.51.96.38
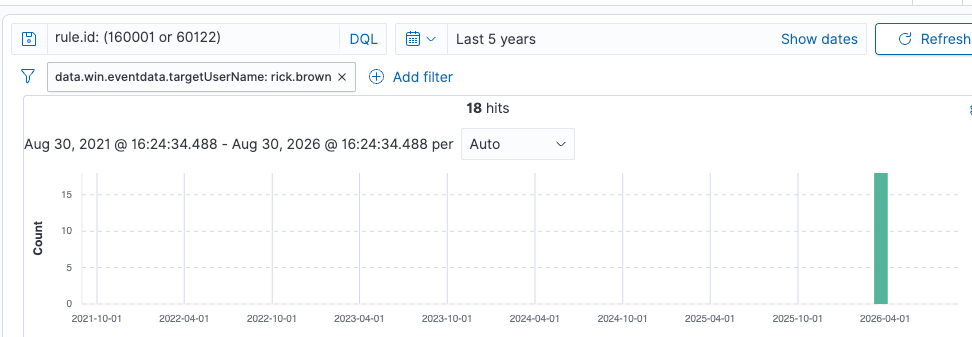
4.1 How many times did the adversary try to log in to rick.brown?
Answer: 18
4.2 Find the definition of the brute force rule in the Wazuh rule files. What is the hidden flag you see at the end of the rule file?
Answer: THM{wazuh_detection_engineer}
Search for Task_5.xml
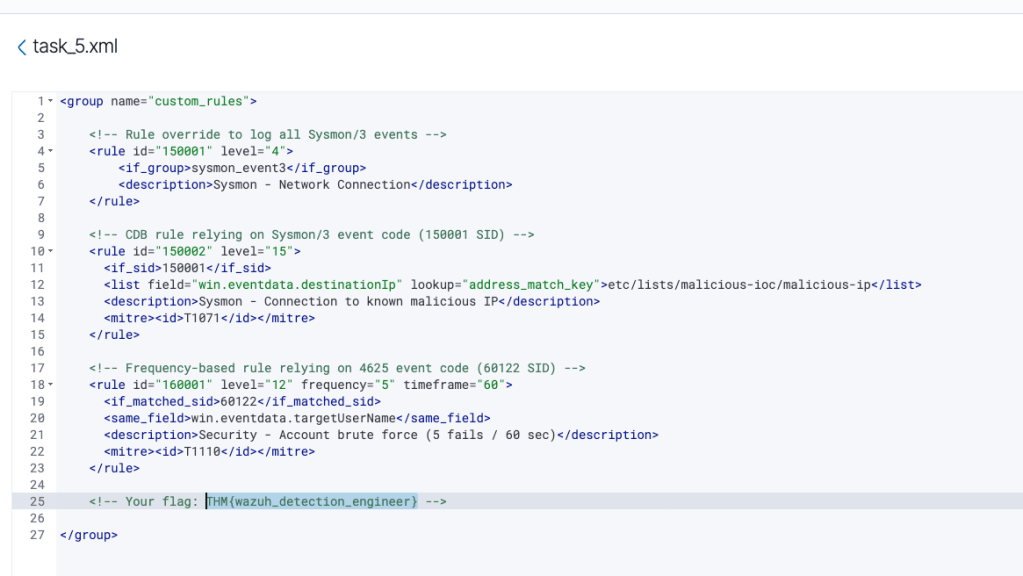
4.3 A CDB rule from the same file caught another adversarial action. Which IP address matched the rule and generated Wazuh alerts?
Again search for Task_5.xml
Answer: 92.118.39.57
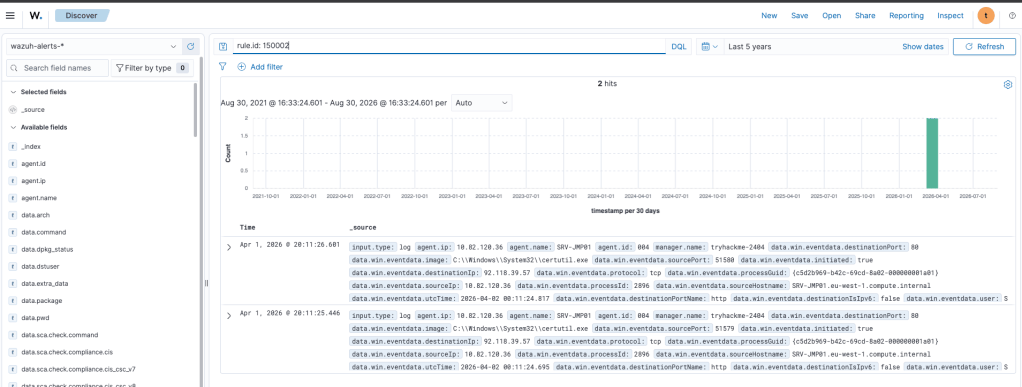
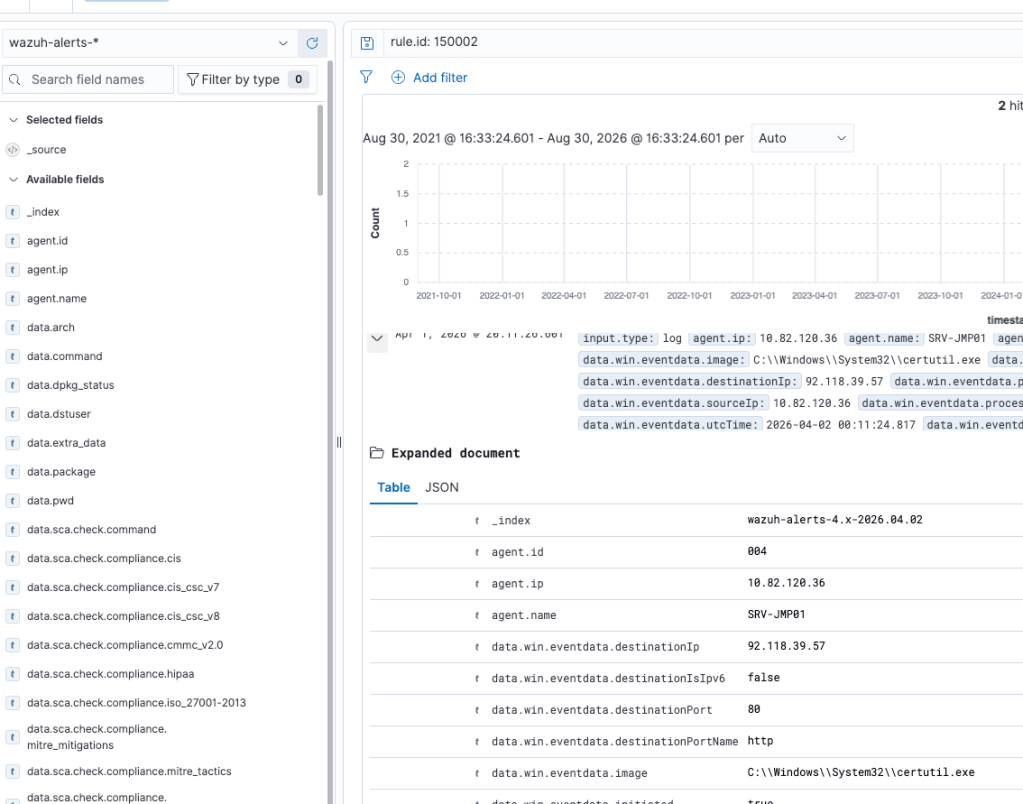
4.4 Which program initiated the connection to the detected IP address? Answer Example: curl.exe
Answer: certutil.exe
5.1 A Linux process creates a file named shell-checker-thm.sh. What rule ID from the task will be triggered?
Answer: 100006
5.2 A Linux process creates a file named malware.elf.What will be the level of the generated alert?
Answer: 12

