The TryHackMe Just a VPN Login Room is classified as free/easy room that uses threat intel sources to determine the response to a room. The room is available at: https://tryhackme.com/room/justavpnlogin
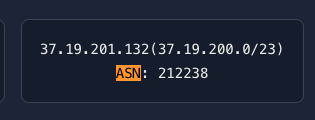
- What is the ASN number related to the IP?
Answer: 212238
2. Which service is offered from this IP?
Answer: VPN
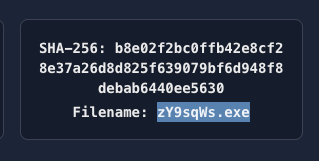
3. What is the filename of the file related to the hash?
Answer: zY9sqWs.exe
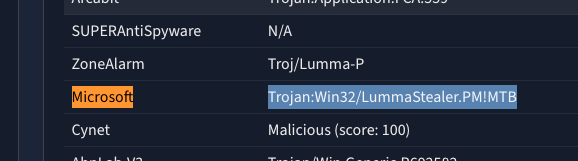
4. What is the threat signature that Microsoft assigned to the file?
Answer: Trojan:Win32/LummaStealer.PM!MTB
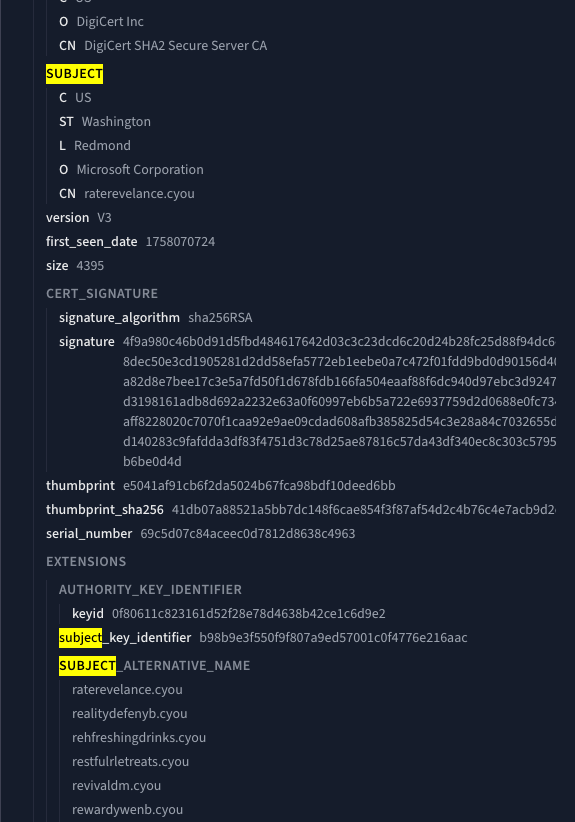
5. One of the contacted domains is part of a large malicious infrastructure cluster.
Based on its HTTPS certificate, how many domains are linked to the same campaign?
Answer: 151
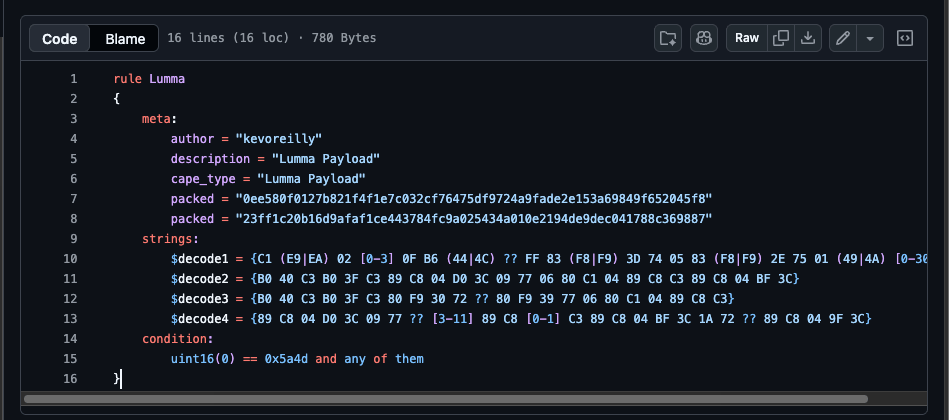
6. The file matches one of the YARA rules made by “kevoreilly”.
What line is present in the rule’s “condition” field?
Answer: uint16(0) == 0x5a4d and any of them
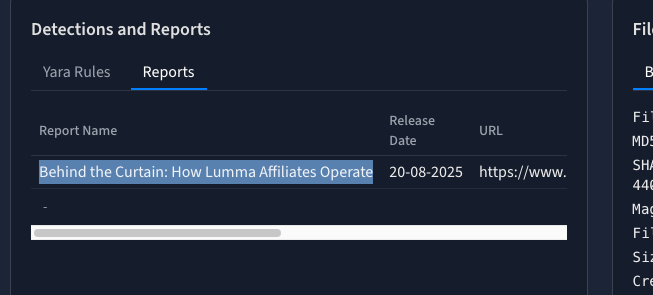
7. The file is also mentioned in a threat intel report.
What is the title of the report mentioning this hash?
Answer: Behind the Curtain: How Lumma Affiliates Operate
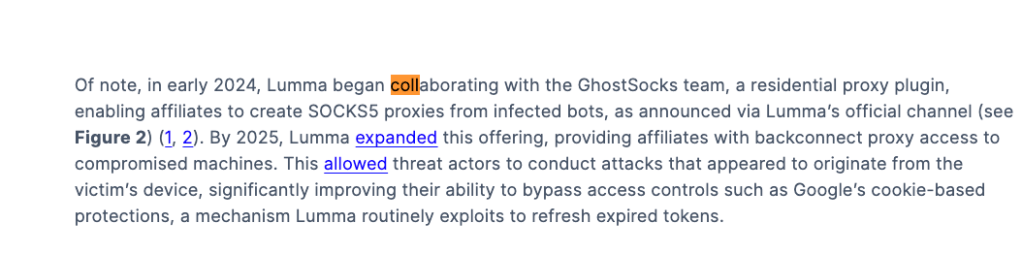
8. Which team did the author of the malware start collaborating with in early 2024?
Answer: GhostSocks
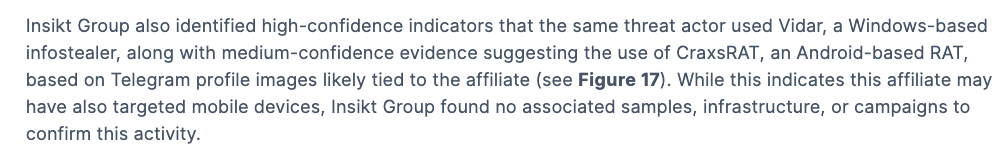
9. A Mexican-based affiliate related to the malware family also uses other infostealers. Which mentioned infostealer targets Android systems?
Answer: CraxsRAT
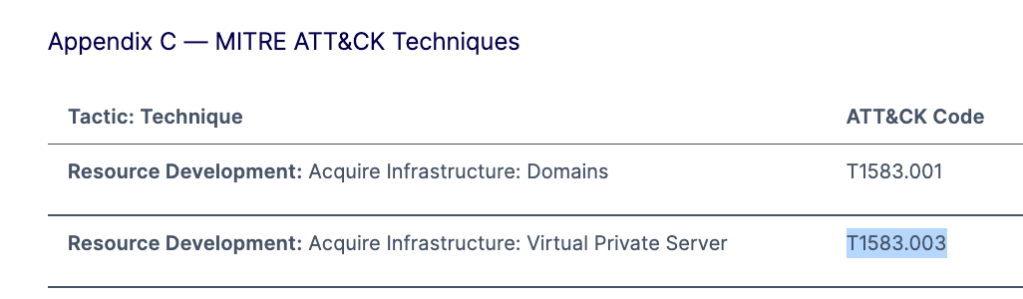
10. The report states that the affiliates behind the malware use the services of AnonRDP. Which Mitre ATT&CK sub-technique does this align with?
Answer: T1583.003