
The TryHackMe Key Artifacts for DFIR Room is the second in a series of room that looks at DFIR for Windows systems. This room concentrates on how and why to extract artifacts from a compromised machine. The room is available at: https://tryhackme.com/room/keyartifactsfordfir
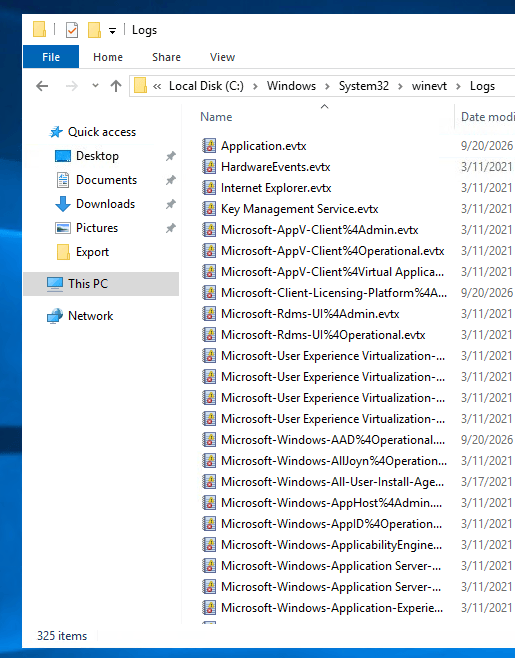
1.1 How many EVTX files are present in the event log folder?
Answer: 325
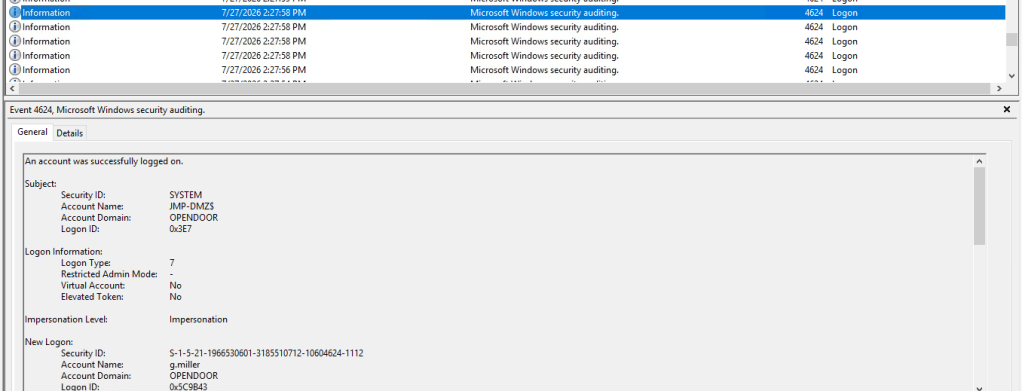
1.2 Export and analyze the Security logs on the DefenseBox. What user was brute-forced according to the 4624/4625 events?
Answer: g.miller
1.3 Are Sysmon logs present to show the process events after the logon? (Yea/Nay)
Answer: Nay
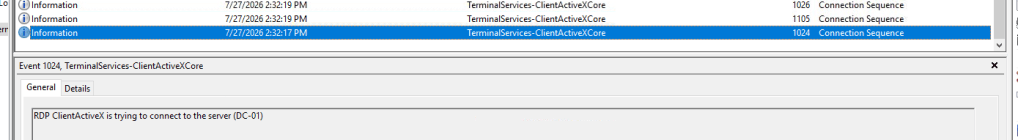
1.4Soon after, the user moved laterally to another host via RDP. What hostname was that according to the RDPClient EVTX logs?
Answer: DC-01
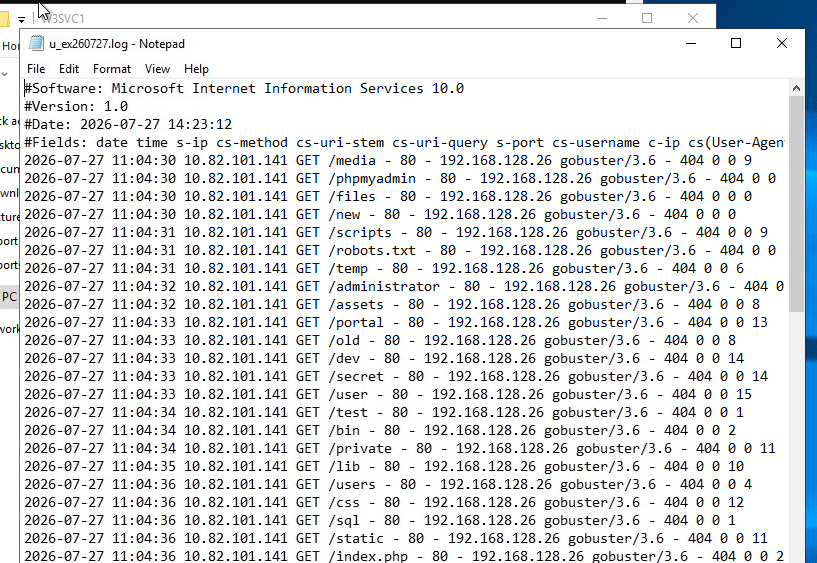
2.1 Before the brute-force, the attacker scanned the local IIS server.What user-agent did the attacker use, according to the web logs?
Answer: gobuster/3.6
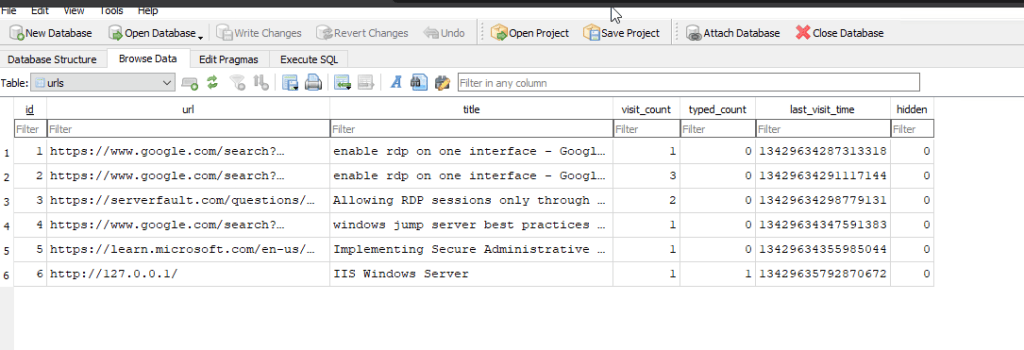
2.2 What was the last Google search of j.stevenson before the attack?
Answer: windows jump server best practices
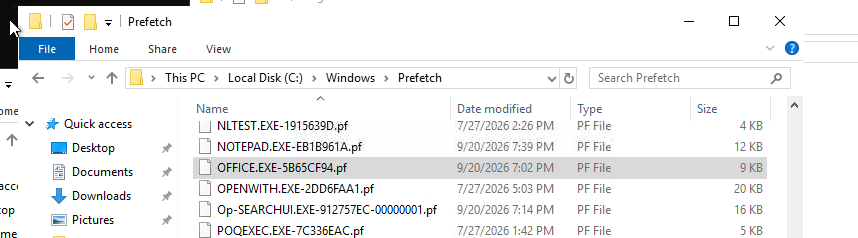
3.1 Prefetch revealed Sliver C2 masking as a Microsoft Office updater. What .pf file confirms its execution from the C:\ProgramData directory?
Answer: OFFICE.EXE-5B65CF94.pf
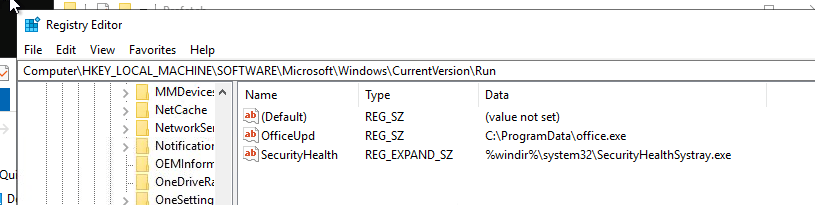
3.2 The C2 persisted in the registry to launch on logon. What is the Run registry key used for persistence?
Answer: OfficeUpd
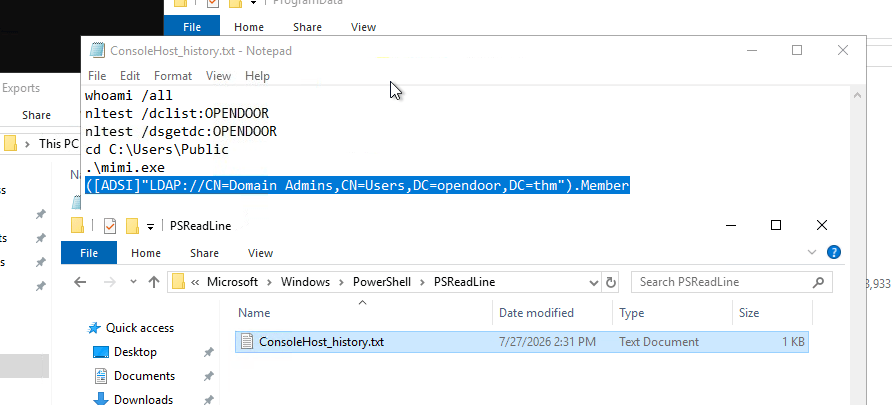
3.3 The adversary also ran PowerShell discovery commands. What is the last command seen in the victim’s history file?
Answer: ([ADSI]”LDAP://CN=Domain Admins,CN=Users,DC=opendoor,DC=thm”).Member
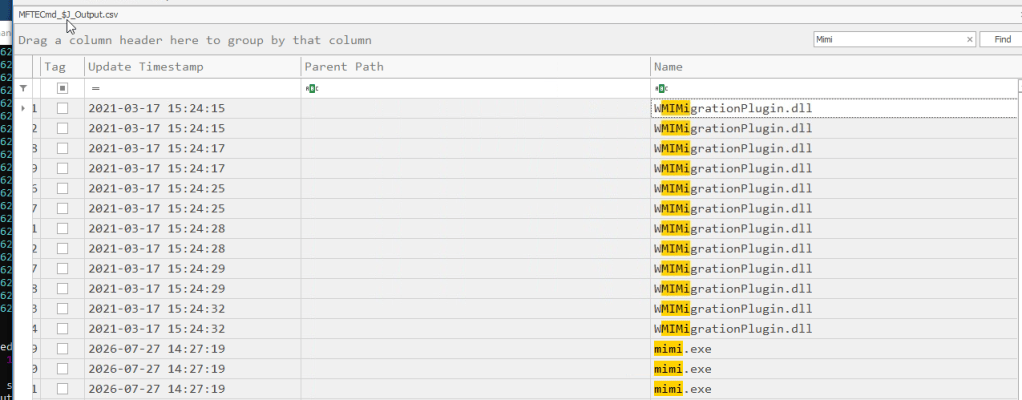
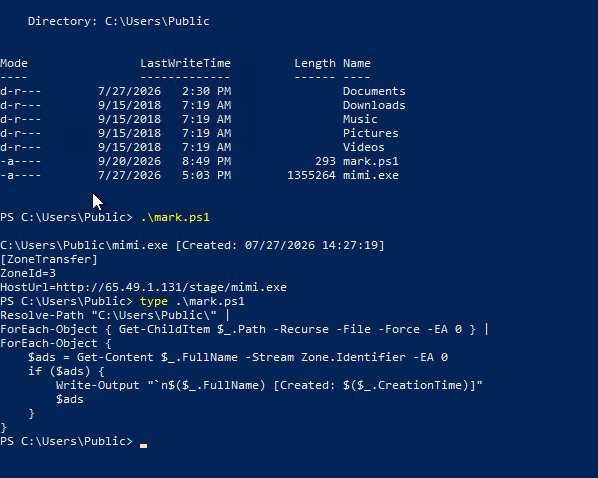
4.1 When was Mimikatz dropped to the Public directory? Answer Example: 2026-07-25 15:30:45
Answer: 2026-07-27 14:27:19
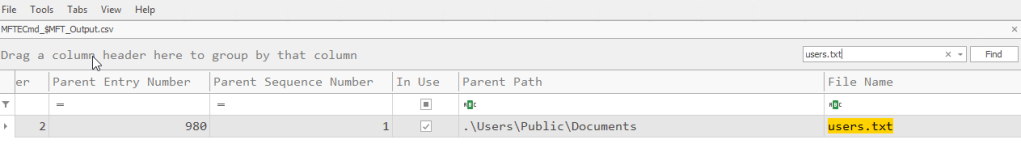
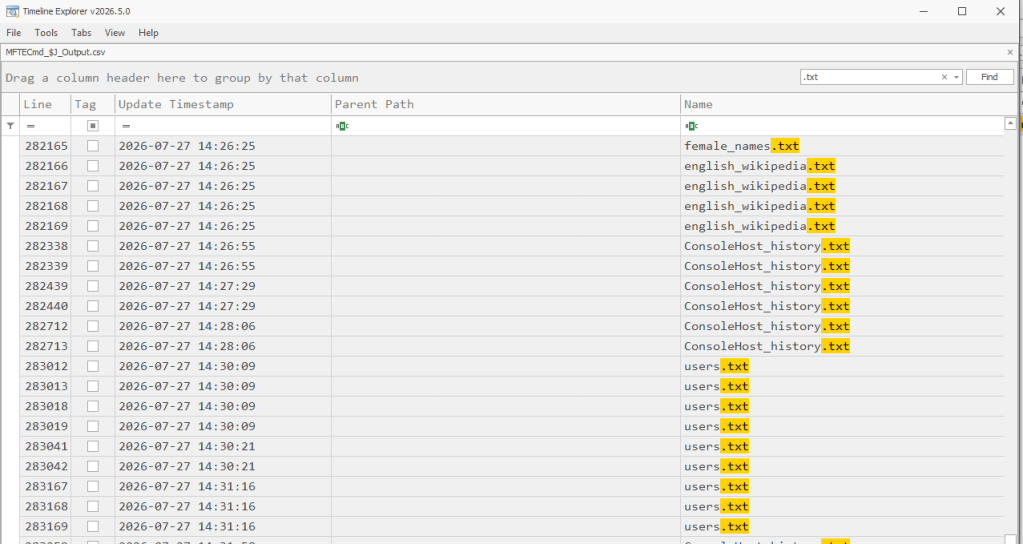
4.2 Three minutes later, Mimikatz dropped a .txt file. What is the absolute path to the created file?
Answer: C:\Users\Public\Documents\users.txt
4.3 The attacker copied Mimikatz without stripping its Mark of the Web. What URL is shown once you adjust and run the script from the task?
Answer: http://65.49.1.131/stage/mimi.exe
5.1 What DFIR tool represents the memory as a virtual filesystem?
Answer: MemProcFS
6.1 Which of the mentioned tools can be used to acquire both NTFS files and disk images?
Answer: FTK Imager

