
The TryHackMe Splunk: Data Manipulation Room is a subscriber/MAX only room from TryHackMe that looks at the different ways to manipulate data in Splunk. The room is available at: https://tryhackme.com/room/splunkdatamanipulation
1.1 What is the full file path to the Splunk directory?
Answer: /opt/splunk
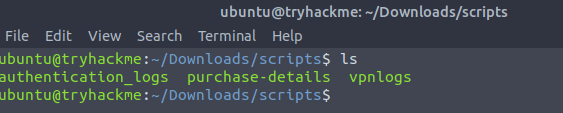
1.2 How many executables are available in the /scripts directory?
Answer: 3
2.1 Which configuration file would you edit to instruct Splunk on what data to ingest?
Answer: inputs.conf
2.2 What is the full path to Splunk’s default configuration files?
Answer: /opt/splunk/etc/system/default
3.1 Which Splunk configuration file is used to define output destinations for indexed data?
Answer: outputs.conf
3.2 Take a look at the example transforms.conf entry below. What line would you add to fields.conf to begin defining the custom field?
[extract_sourceip]
REGEX = User\s+(\S+)\s+logged
FORMAT = SourceIP::$1
Answer: [SourceIP]
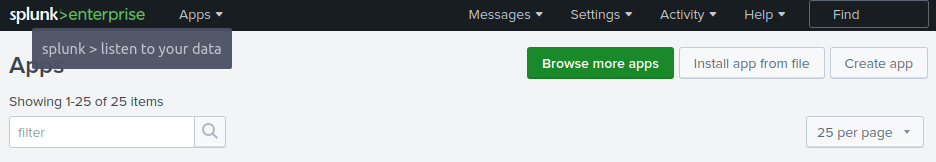
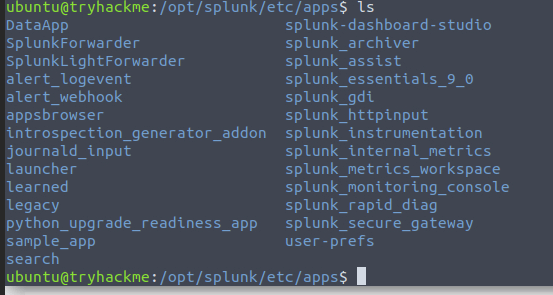
4.1 When Splunk is first installed, how many default applications are available?
Answer: 25
4.2 What is the full path to your newly created application directory?
Answer: /opt/splunk/etc/apps/DataApp
5.1 Which configuration file is used to specify parsing rules?
Answer: props.conf
5.2 What regex pattern is used in the case above to break the events?
Answer: (CONNECT|DISCONNECT)
6.1 Which configuration setting was used to ensure Splunk breaks the event boundary before the specified regex pattern?
Answer: BREAK_ONLY_BEFORE
6.2 Which regex pattern did you use in your props.conf file to specify where Splunk should break the events?
Answer: \[Authentication\]
7.1 Which payment security standard did you adhere to by masking sensitive customer credit card information?
Answer: PCI DSS
7.2 What is the full value of the SEDCMD you used in props.conf?
Answer:
8.1 After performing field extraction on the purchase logs, how many User field values exist within the event data?
Answer: 14
8.2 How many unique masked CC_Number field values were extracted from the events?
Answer: 10

